The Architecture of Proof AI Governance Framework
Welcome to the Architecture of Proof, a comprehensive AI governance lifecycle designed for the age of probabilistic systems.
This framework moves beyond "AI safety" as a vague concept and into AI control as a systems architecture. It is designed for high-stakes domains: finance, healthcare, cybersecurity, and industrial automation: where "close enough" isn't an option.
How Does an Organization Mature Across the 4-Stage AI Governance Lifecycle?
The Architecture of Proof isn't just a stack; it’s a journey from Probabilistic Uncertainty to Deterministic Evidence. Most organizations are stuck in Stage 1 or 2. Moving between stages requires Evidence-Based Promotion. Explore the full audit criteria in the 4-Stage AI Maturity Model.
Accuracy-focused, black-box, no audit trail. Typical of sandbox environments where speed outpaces evidence.
Can reconstruct exactly what happened using basic logging and Replayability.
Uses Control Tiers and automated escalation to govern the AI's "leash length."
What Are the Core Layers of the 7-Layer Architecture Stack?
To advance through the maturity curve, engineering organizations must operationalize the core architectural layers:
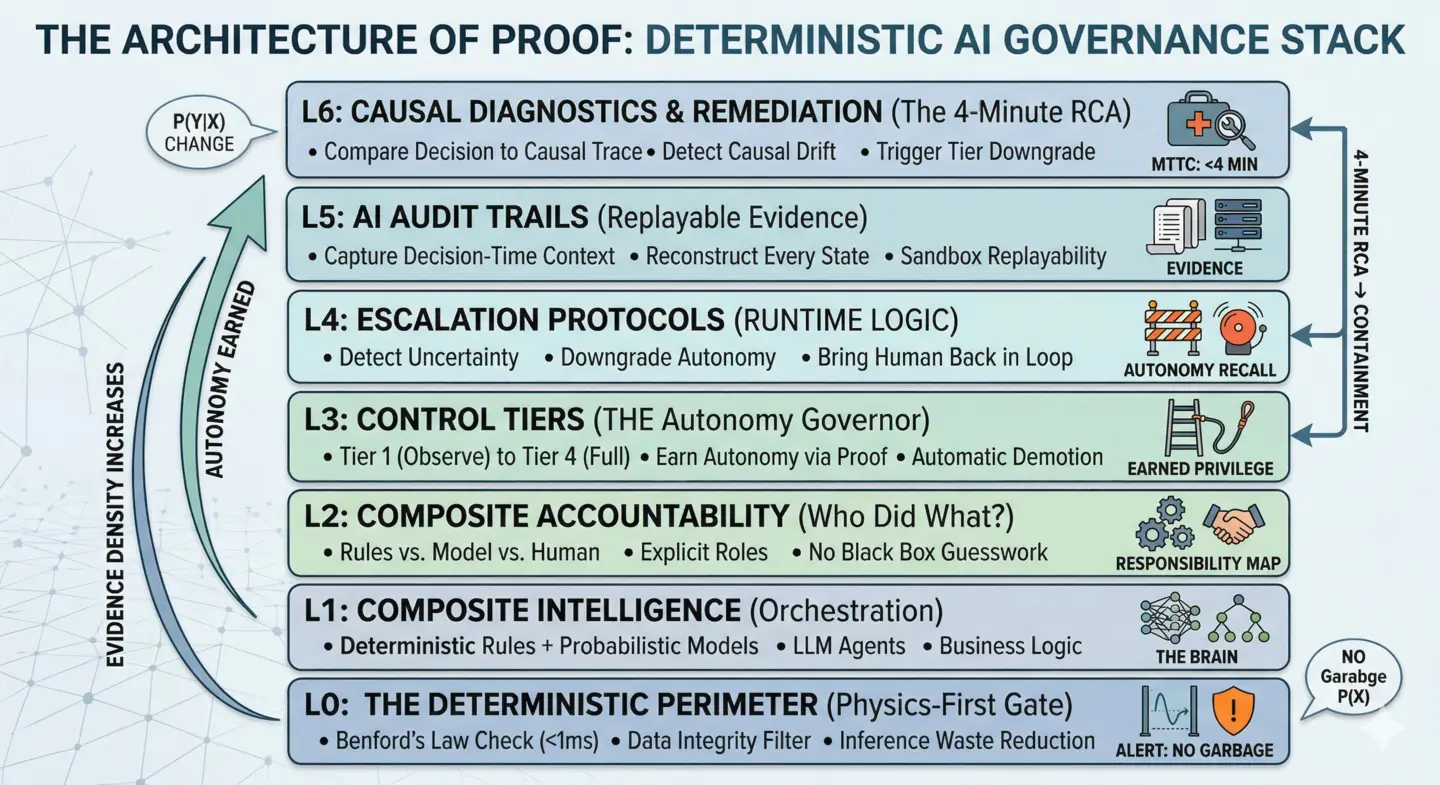
| Architectural Layer | Systems Focus | Operational Mechanism & Invariant |
|---|---|---|
| Layer 0: Deterministic Perimeter | Physics-First Pre-Inference Validation | Sub-millisecond statistical and structural filters (e.g., Benford's Law, schema typing) drop corrupted, adversarial, or out-of-distribution payloads before neural inference. |
| Layer 1: Composite Intelligence | Multi-Paradigm Orchestration | Choreographs deterministic rule engines, probabilistic foundation models, and human supervisors into a cohesive decision pipeline. |
| Layer 2: Composite Accountability | Multi-Actor Contractual Defensibility | Machine-readable pre- and post-conditions governing interfaces across automated agents, models, and human operators. |
| Layer 3: Control Tiers | Bounded Autonomy Assignment | Four standardized operating tiers (Tier 0 to Tier 3) establishing explicit operational boundaries and blast perimeters. |
| Layer 4: Escalation Protocols | Dynamic Autonomy Demotion | Runtime state machines that detect anomalies, trip circuit breakers, and downgrade autonomy to human review before failure cascade. |
| Layer 5: Audit Trails for AI | Deterministic Replayability | Append-only Decision State Vectors (DSV) capturing prompt hashes, context chunk IDs, model seeds, and runtime parameters. |
| Layer 6: Causal Diagnostics & Remediation | Root Cause Attribution (<4 min) | Counterfactual replay trees mapping failures to specific data drift, retrieval corruption, or rule engine boundary degradation. |
The PM's 7-Layer Architecture Gate: 5 Verification Questions for Sprint & PRD Reviews
To ensure product managers can evaluate whether their autonomous system satisfies enterprise defense requirements before production release, review this verification matrix:
| Layer Boundary | Architectural Verification Check | Red Flag Condition (Release Blocker) | PM Mandate & Action |
|---|---|---|---|
| 1. Ingress Perimeter (L0) | Are incoming payloads validated via deterministic schema and statistical checks before LLM invocation? | Raw user strings pass directly to model prompts without structure or type validation. | Mandate Layer 0 input filter; reject unvalidated payloads at the API gateway. |
| 2. Contractual Postconditions (L2) | Does every agent action output conform to typed schemas with invariant bounds before DB mutation? | Free-form natural language outputs directly trigger downstream database commits. | Enforce JSON Schema / Zod postcondition validation before committing state mutations. |
| 3. Bounded Autonomy (L3) | Is the workflow assigned an explicit Control Tier with clear financial and operational blast perimeters? | High-liability transactions execute under unconstrained Tier 3 autonomy without human oversight. | Assign appropriate Control Tier; force Tier 2 human sign-off on transactions over threshold. |
| 4. Circuit Breakers (L4) | Do unexpected model outputs, low confidence scores, or latency spikes trigger automated rollback? | The system retries failing probabilistic prompts indefinitely without human escalation. | Configure runtime circuit breakers; downgrade autonomy to fallback rules on anomaly. |
| 5. Causal Audit Trail (L5-L6) | Does every consequential decision emit a cryptographic receipt containing prompt, chunk, and seed hashes? | Postmortems require manual reconstruction from unstructured log lake text dumps. | Mandate Decision State Vector emission; verify 4-minute replayability in staging. |
Why Implement This Architecture?
Deploying the seven-layer governance stack transforms unpredictable black-box agent behavior into a transparent glass-box system:
| Architectural Property | Black-Box Pilot Mode | Glass-Box Architecture of Proof |
|---|---|---|
| Operational Traceability | Ephemeral chat logs; lost context; non-reproducible outcomes. | Cryptographically anchored decision state vectors supporting bit-level counterfactual replay. |
| Execution Reliability | Probabilistic models operate directly on raw external inputs with unhedged failure risk. | Deterministic perimeters and invariant boundaries filter corrupted data before inference. |
| Governance Defensibility | Ambiguous blame allocation across third-party models, prompt engineers, and users. | Enforceable component contracts assign legal and operational accountability to specific system components. |
How Should Engineering Teams Navigate the Framework Monograph Tracks?
To explore specific operational implementations, follow these core reading tracks across the monograph library:
1. Architecture & Infrastructure
- How to Write AI Component Contracts: Operationalizing strict interface boundaries between probabilistic models and business logic.
- The Deterministic Perimeter: Filtering anomalous inputs before inference to protect latency and margins.
- Audit Trails for Probabilistic Systems: Architecting immutable decision logs that support deterministic post-mortems.
2. Product Strategy & Leadership
- JTBD to Delegations to be Supervised: Moving from conversational prompts to bounded, supervisable workflows.
- The Unit Economics of the Retrieved Chunk: Balancing context retrieval precision, latency budgets, and compute margins.
- AI Platform Capability Test: Evaluating platform boundaries, vendor lock-in, and infrastructure leverage.
3. Evaluation, Evidence & Governance
- How to Build a Governed AI Evaluation System: Replacing composite scoring with constrained optimization and four-layer triangulation.
- Goodhart’s Law in Generative AI: Why AI systems optimize for metrics at the expense of true product quality.
- Five Enterprise AI Governance Failures: Case studies and post-mortems of organizational breakdowns in production AI.
- Adversarial Governance: Designing independent oversight mechanisms that challenge model promotion assumptions.
4. Legal, Liability & Incident Response
- AI Incident Response Plan: The Golden Hour: Deterministic containment protocols when production models deviate.
- The Multi-Agent Liability Trap: Structuring legal and operational responsibility across cascading agent architectures.
- AI Accountability Architecture: Transforming corporate policy into verifiable, auditable system boundaries.
The Adversarial Stress-Test: What Could Break the Architecture of Proof?
1. What is the strongest argument against this approach?
The Objection: Imposing a seven-layer governance stack with deterministic perimeters, component contracts, and append-only audit logs creates massive engineering overhead, slows development velocity, and suffocates agile experimentation in early-stage product development.
The Practical Resolution: Implement the stack progressively using a tiered adoption model. Early prototypes start at Stage 1 with basic perimeter schema typing and token budgeting. Full audit logging (Layer 5) and contractual component boundaries (Layer 2) are required only when an agent is promoted to Tier 2 (Act with Breakers) or Tier 3 (High Liability), ensuring governance overhead scales proportionally with autonomous operational risk.
2. Under what circumstances would this fail?
The Failure Mechanism: The architecture fails when deterministic perimeter checks (Layer 0) introduce false negatives by rejecting novel, valid out-of-distribution enterprise inputs, or when the storage and indexing costs of append-only Decision State Vectors (Layer 5) scale unsustainably across millions of daily high-throughput transactions.
The Practical Resolution: Enforce dual-path perimeter routing and tiered audit compaction. Out-of-distribution inputs that fail fast statistical perimeter tests are not dropped; they are routed to a low-privilege quarantine sandbox for asynchronous human adjudication. For audit logging, store full token transcripts in short-retention ephemeral buffers (30 days) while archiving lightweight cryptographic state hashes and input-output coordinates in permanent cold storage.
3. What would a skeptical customer, client, or colleague object to?
The Skeptical Pushback: Enterprise executives often dismiss multi-layered governance frameworks as academic complexity, arguing that foundation model providers will integrate native guardrails and alignment improvements that render custom architecture redundant.
The Practical Resolution: Demonstrate the fundamental boundary distinction: foundation model alignment operates probabilistically within model weights, whereas enterprise liability requires deterministic guarantees outside model weights. A model vendor cannot indemnify an enterprise against regulatory non-compliance, statutory wiretap damages, or financial transaction errors caused by upstream retrieval poisoning or agentic hallucination. External architectural control remains the sole legally defensible perimeter.
4. Which alternative deserves more consideration?
The Counter-Architecture: Pure End-to-End Neural Orchestration without explicit intermediate rule boundaries. Proponents argue that multi-modal foundation models trained with extensive reinforcement learning can autonomously self-correct, negotiate API calls, and handle edge cases more fluidly than rigid rule-model composite architectures.
The Practical Resolution: Adopt a hybrid compartmentalized execution topology. Allow flexible neural models to propose complex multi-step plans and draft tool invocations, but mandate that all state-mutating actions (database writes, financial transactions, external emails) execute through deterministic validation proxies that enforce invariant schema checks and business rule boundaries prior to database commit.
5. What am I assuming that may not be true?
The Latent Vulnerability: We are assuming that enterprise organizations possess the operational discipline and cross-functional coordination required to maintain component contracts, monitor causal drift, and adjudicate escalations within four-minute operational windows.
The Practical Resolution: Automate governance enforcement directly within CI/CD pipelines and infrastructure orchestrators. Treat component contracts as compiled software artifacts that fail pull request builds if test coverage or schema invariants are breached. Escalations that do not receive timely human adjudication automatically trigger safe state rollbacks and temporary autonomy demotion, preventing unmonitored agent drift.
What Is the Core Architecture Invariant?
The Architecture of Proof establishes enforceable engineering boundaries around probabilistic models through deterministic perimeters, component contracts, and causal decision ledgers.
Subscribe to the Architecture of Proof Dispatch
Rigorous, decision-forcing systems engineering and AI governance monographs for technical leaders. Delivered periodically, zero spam.